EDR vs XDR vs MDR: What’s the Difference?
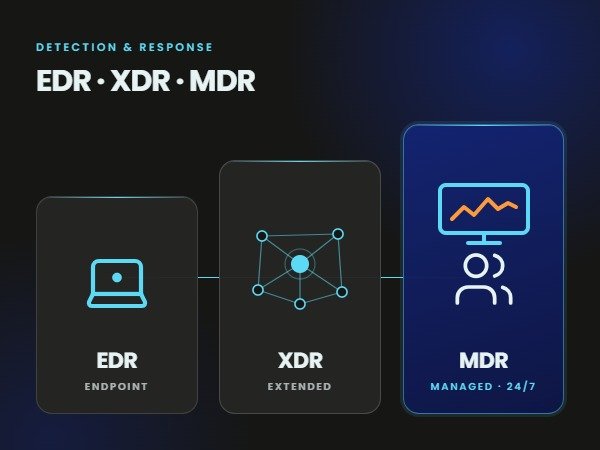
EDR protects endpoints, XDR correlates signals across the environment, and MDR is the service that operates them. See how they differ and which one you need.
What is a Red Team? How adversary emulation works
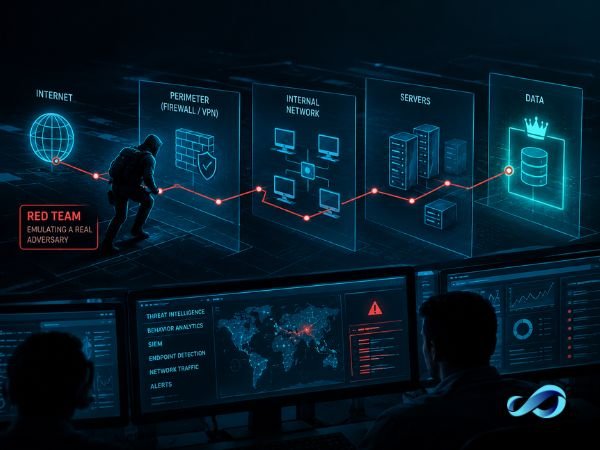
A Red Team simulates a real adversary to test whether your company can detect and respond to a targeted attack. Learn how it works and when you are ready.
Information Security for the Financial sector: Regulation and risks
The financial sector is the top target for cyberattacks. Learn the main risks, the key regulations (PCI-DSS, DORA, BACEN), and how to build a resilient program.
Types of Pentest and when to use each
The main types of pentest are external, internal, application, and social engineering. Learn what each one tests, what it simulates, and when to use each.
Brasil: Como o Stark Bank evoluiu o contexto de Segurança digital diante da era da IA
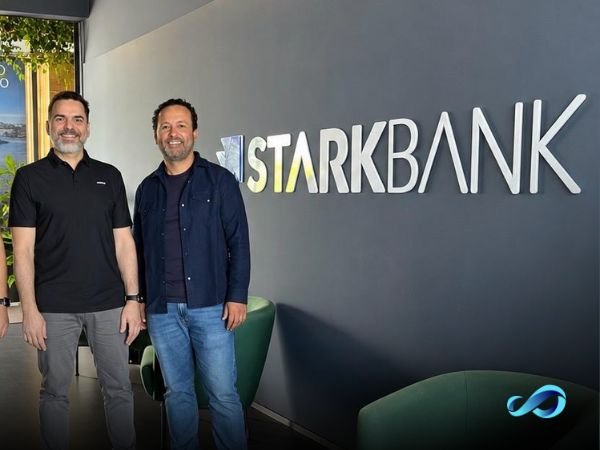
Veja como o Stark Bank adaptou sua estratégia de segurança digital aos novos riscos e oportunidades trazidos pela inteligência artificial.
SIEM vs Managed SOC: What’s the Difference?
A SIEM is a tool that collects and correlates logs. A managed SOC is a service that monitors, detects, and responds. See the difference and which you need.