Offensive security, 24/7 operations, exposure management, governance and fraud prevention in a single ecosystem.
We were founded in Chile in 2023 by hackers and specialized consultants. Today we protect critical organizations across Latin America and the United States, and we measure risk against real attacker behavior.
We were founded in Chile with one conviction: defense only holds when it has been tested by people who break systems for a living. So instead of competing on dashboards, we built a company around offensive proof.
Today our teams operate locally in three countries. We run red team engagements, adversary emulation and continuous exposure testing, then feed what we find into AI-driven security operations and threat intelligence. The result is a security posture measured against real attacker behavior, not compliance checklists.
We work with organizations where a breach is not an inconvenience but an existential event: financial institutions, critical infrastructure, legal, retail and technology leaders across the region.
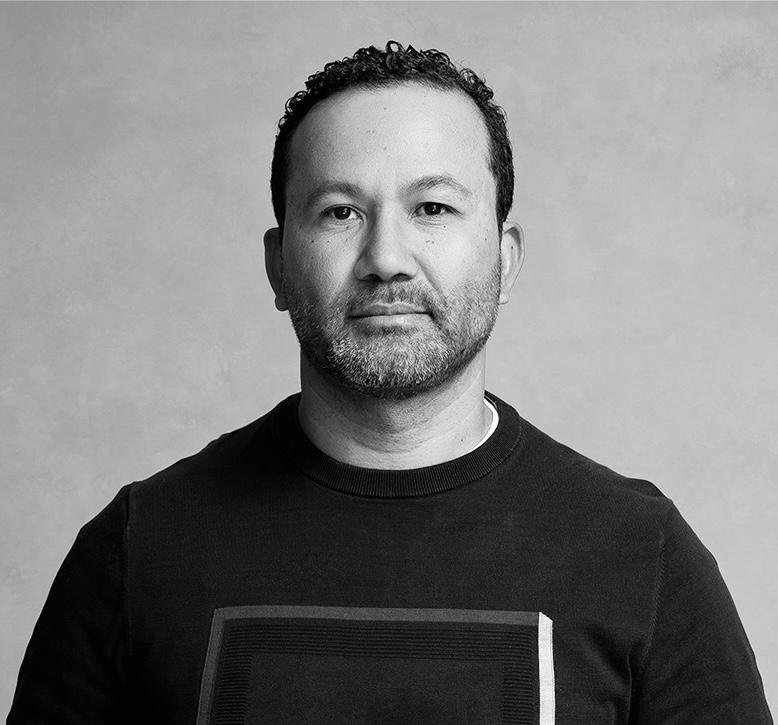
Marcos Reis served as CISO at Itaú Chile, where he led the Cybersecurity and Fraud Prevention program and established the bank’s Security by Design baseline. He was also Executive Director of Operational Risk at BTG Pactual.
Before that, he held IT Risk and Audit roles at Santander, ABN AMRO and Bank of America. In 2023 he founded Mercurius and grew it from an ethical hacking firm into an AI-driven cybersecurity company operating in three countries.
We report the uncomfortable truth, because it is the only version worth paying for. These are the commitments behind every engagement.
To be the reference critical organizations across LATAM turn to when they need to know — not assume — how they’d hold up against a determined attacker.
Give security and executive leaders a clear, tested view of their real exposure — so risk stops being abstract and becomes something they can measure, prioritize and reduce.
Our offensive mindset follows methodological rigor. We work with analytical depth and evidence-based execution, so every finding carries strategic weight.
Our decisions affect the continuity, governance and reputation of the organizations we serve. We weigh systemic impact, prioritize critical risk and bring security into business strategy.
Security is movement. We update techniques, revise processes and adapt strategy to keep control in environments that change every day.
Exposure intelligence feeds defense and fraud prevention. One team owns the whole cycle, from the first finding to the board report.
Offensive Security
Pentest and Red team including OT/ICS, continuous PTaaS, AppSec and code review, with retesting after every fix.
SOC AI 24/7
SOC AI with agentic investigation and N1 to N3 analysts, DFIR activated within 2 hours, Zero Trust from network to endpoint.
Threat intelligence and vulnerabilities
Threat intelligence, attack surface and vulnerability management merged into one priorization: a short list of what is actually exploitable.
Cyber Governance
Continuous evidence for ISO 27001, SOC 2, PCI-DSS and LGPD, vCISO, privacy and data governance, with risk expressed in business value.
Costumer fraud journey
Chained layers from pre-attack to scan: onboarding, session, critical actions and transactions, with every fraud signal sent to the SOC AI.
Six certified analysts work in five squads by specialty. Each analyst leads one front and backs up another, with a transversal Purple Team validating detection and response across all of them.
Cloud, IAM and workloads
Web AppSec and advanced exploitation
APIs and integrations
AI, LLM and agent security
Network, Active Directory and red team
OSCP
OSCP+
OSWE
OSCE
CRTO
CRTP
eWPTX
CPTS
CRISC
CISM
MITRE ATT&CK: Adversary tactics and techniques that shape our emulation and detection
OWASP: Testing methodology for web, API and mobile applications
ISO/IEC 27001: Information security controls we assess and help implement
SOC 2: Trust services criteria we map evidence and controls against
Frameworks we build on. They do not represent Mercurius certifications.
Our headquarters are in Santiago. We serve Brazil from São Paulo and the United States from Miami, in Portuguese, Spanish and English, with security operations running 24/7.
We buy directly from the manufacturers, with no distributor in between, and our team deploys and operates every platform under SLA.
Two agentic SOC platforms, matched to your size and stack. AI-driven triage and response that reduce analyst workload and time to containment.
Our own free scanners. Cactus maps your external attack surface. Hawk reveals leaked credentials and dark web exposure.
Our solutions are listed on both marketplaces, so you can buy through your existing cloud commitments and credits.
Clients in financial services, mining, energy, media, logistics, public sector and more, in Chile, Brazil and the United States.
And the next one could be you
Talk to our team about a scoped offensive engagement, AI SOC or threat intelligence for your organization.