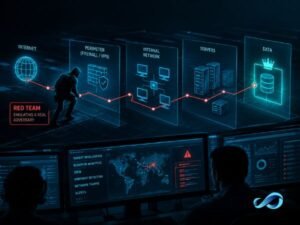
What is a Red Team? How adversary emulation works
A Red Team simulates a real adversary to test whether your company can detect and respond to a targeted attack. Learn how it works and when you are ready.
Threat reports, research papers, webinars and whitepapers from the Mercurius security team — staying ahead of the adversary.
A Red Team simulates a real adversary to test whether your company can detect and respond to a targeted attack. Learn how it works and when you are ready.
The financial sector is the top target for cyberattacks. Learn the main risks, the key regulations (PCI-DSS, DORA, BACEN), and how to build a resilient program.
The main types of pentest are external, internal, application, and social engineering. Learn what each one tests, what it simulates, and when to use each.
Veja como o Stark Bank adaptou sua estratégia de segurança digital aos novos riscos e oportunidades trazidos pela inteligência artificial.
A SIEM is a tool that collects and correlates logs. A managed SOC is a service that monitors, detects, and responds. See the difference and which you need.
Do nosso stand no Mind The Sec 2026, cinco temas dominaram as conversas com CISOs e líderes de TI. Nossa leitura de cada um, com o que vemos operando na prática.
AI in the SOC automates alert triage and investigation, cutting detection time and analyst fatigue. Learn how it works, its limits, and its impact on security.
A managed SOC gives your company 24/7 threat monitoring and response run by an external team. Learn how it works, the technology, and when you need one.
A CVE is the public identifier for a known vulnerability. Learn how the system works, the CVE lifecycle, how CVE differs from CVSS and KEV, and how to use them.